

Instant Download CompTIA : SY0-501日本語 Exam Dumps

Updated: Oct 24, 2026
No. of Questions: 715 Questions & Answers
Download Limit: Unlimited
This exam has been stopped to register, new exam code replace: SY0-701-JPN
Instant Download: Upon successful payment, Our systems will automatically send the product you have purchased to your mailbox by email. (If not received within 12 hours, please contact us. Note: don't forget to check your spam.)
100% Money Back Guarantee
Lead1Pass has an unprecedented 99.6% first time pass rate among our customers.  We're so confident of our products that we provide no hassle product exchange.
- Best exam practice material
- Three formats are optional
- Learn anywhere, anytime
- 100% Safe shopping experience
- 10 years of excellence
- 365 Days Free Updates
SY0-501日本語 Online Test Engine
- Online Tool, Convenient, easy to study.
- SY0-501日本語 Practice Online Anytime
- Instant Online Access SY0-501日本語 Dumps
- Supports All Web Browsers
- Test History and Performance Review
- Supports Windows / Mac / Android / iOS, etc.
- Try Online Engine Demo
- Total Questions: 715
- Updated on: Oct 24, 2026
- Price: $79.00
SY0-501日本語 Desktop Test Engine
- Installable Software Application
- Practice Offline Anytime
- Builds SY0-501日本語 Exam Confidence
- Simulates Real SY0-501日本語 Exam Environment
- Two Modes For SY0-501日本語 Practice
- Supports MS Operating System
- Software Screenshots
- Total Questions: 715
- Updated on: Oct 24, 2026
- Price: $79.00
SY0-501日本語 PDF Practice Q&A's
- Printable SY0-501日本語 PDF Format
- Instant Access to Download SY0-501日本語 PDF
- Study Anywhere, Anytime
- Prepared by CompTIA Experts
- Free SY0-501日本語 PDF Demo Available
- 365 Days Free Updates
- Download Q&A's Demo
- Total Questions: 715
- Updated on: Oct 24, 2026
- Price: $79.00
In 2026, carrying paper study guides feels like a relic; the Lead1Pass SY0-501日本語 package downloads to your phone in about a minute after purchase and puts 715 practice questions for the SY0-501日本語 exam within reach of every spare five minutes.
CompTIA SY0-501日本語 Exam Overview:
| Certification Vendor: | CompTIA |
|---|---|
| Exam Name: | CompTIA Security+ Certification Exam SY0-501 |
| Exam Number: | SY0-501 |
| Exam Duration: | 90 minutes |
| Available Languages: | Japanese, Portuguese, English |
| Exam Format: | Performance-based questions, Multiple-choice questions |
| Related Certifications: | CompTIA Network+ CompTIA A+ |
| Certificate Validity Period: | 3 years (certification validity from passing date) |
| Passing Score: | 750 (on a scale of 100-900) |
| Exam Price: | USD $339 (varies by region) |
| Real Exam Qty: | Maximum 90 questions |
| Recommended Training: | CompTIA Security+ Official Training |
| Exam Registration: | CompTIA Exam Registration (Pearson VUE) CompTIA Security+ Official Page |
| Sample Questions: | DOWNLOAD DEMO |
| Exam Way: | Test center (Pearson VUE) or online proctored exam |
| Pre Condition: | No mandatory prerequisites; recommended experience of 2 years in IT administration with a security focus or CompTIA Network+ certification knowledge. |
| Official Syllabus URL: | https://www.comptia.org/certifications/security |
CompTIA SY0-501日本語 Exam Syllabus Topics:
| Section | Weight | Objectives |
|---|---|---|
| Architecture and Design | 15% | - Secure network architecture concepts
|
| Governance, Risk, and Compliance | 21% | - Risk management concepts
|
| Attacks, Threats, and Vulnerabilities | 21% | - Threat actors and attack types
|
| Operations and Incident Response | 20% | - Security operations
|
| Implementation | 23% | - Secure infrastructure implementation
|
CompTIA Security+ Certification Exam (SY0-501日本語版) Essentials: What Candidates Ask
- Operations and Incident Response (20%)
- Implementation (23%)
- Architecture and Design (15%)
CompTIA Security+ Certification Exam (SY0-501日本語版) Sample Questions:
新入社員のアンは、不明なソースから、提供されたリンクをクリックして会社のプロファイルを更新する必要があることを示す電子メールを受け取りました。アンがリンクをクリックすると、コマンドプロンプトが表示され、次の出力が表示されます。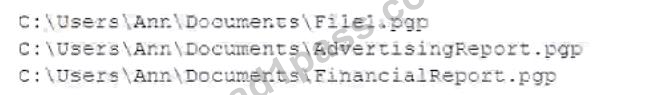
次の種類のマルウェアのどれが実行されましたか?
- A. Adware
- B. Virus
- C. Ransomware
- D. Spyware
Correct Answer: C 🗳️
ネットワーク管理者には、脆弱性スキャンから次の出力が提供されました。
ネットワーク管理者は、企業に対する全体的なリスクに基づいて修復作業に優先順位を付けるように指示されています。次のプラグインIDのどれを最初に修復する必要がありますか?
- A. 14
- B. 12
- C. 11
- D. 10
- E. 13
Correct Answer: E 🗳️
次の攻撃のうち、適切なデータ保持ポリシーによって軽減できるのはどれですか?
- A. Dumpster diving
- B. Man-in-the-browser
- C. Spear phishing
- D. Watering hole
Correct Answer: A 🗳️
タスク:ファイアウォールを構成して(表に記入)、次の4つのルールを許可します。
*アカウンティングコンピューターに管理サーバーへのHTTPSアクセスのみを許可します。
* HRコンピューターがSCPを介してサーバー2システムと通信できるようにするだけです。
* ITコンピューターが管理サーバー1と管理サーバー2の両方にアクセスできるようにする

Correct Answer:
Use the following answer for this simulation task.
Below table has all the answers required for this question.
firewall rules act like ACLs, and they are used to dictate what traffic can pass between the firewall and the internal network. Three possible actions can be taken based on the rule's criteria:
Block the connection Allow the connection
Allow the connection only if it is secured
TCP is responsible for providing a reliable, one-to-one, connection-oriented session. TCP establishes a connection and ensures that the other end receives any packets sent.
Two hosts communicate packet results with each other. TCP also ensures that packets are decoded and sequenced properly. This connection is persistent during the session.
When the session ends, the connection is torn down.
UDP provides an unreliable connectionless communication method between hosts. UDP is considered a best-effort protocol, but it's considerably faster than TCP.
The sessions don't establish a synchronized session like the kind used in TCP, and UDP doesn't guarantee error-free communications.
The primary purpose of UDP is to send small packets of information.
The application is responsible for acknowledging the correct reception of the dat a. Port 22 is used by both SSH and SCP with UDP.
Port 443 is used for secure web connections? HTTPS and is a TCP port.
Thus to make sure only the Accounting computer has HTTPS access to the Administrative server you should use TCP port 443 and set the rule to allow communication between 10.4.255.10/24 (Accounting) and 10.4.255.101 (Administrative server1) Thus to make sure that only the HR computer has access to Server2 over SCP you need use of TCP port 22 and set the rule to allow communication between 10.4.255.10/23 (HR) and 10.4.255.2 (server2) Thus to make sure that the IT computer can access both the Administrative servers you need to use a port and accompanying port number and set the rule to allow communication between: 10.4.255.10.25 (IT computer) and 10.4.255.101 (Administrative server1)
10.4.255.10.25 (IT computer) and 10.4.255.102 (Administrative server2)
セキュリティ管理者が、組織のWebサーバーにアクセスできない顧客について、ヘルプデスクから複数の電話を受けました。ログファイルを確認すると、セキュリティ管理者は、複数のIPアドレスから複数のオープンリクエストが行われ、システムリソースを消費していると判断します。このBESTは次のどの攻撃タイプを説明していますか?
- A. DDoS
- B. ゼロデイ
- C. DoS
- D. 論理爆弾
Correct Answer: A 🗳️
Viewing page 1 out of 143 pages.
Viewing questions 1-5 out of 715 questions.
 0 Customer ReviewsCustomers Feedback (* Some similar or old comments have been hidden.)
Instant Download SY0-501日本語
After Payment, our system will send you the products you purchase in mailbox in a minute after payment. If not received within 2 hours, please contact us.
365 Days Free Updates
Free update is available within 365 days after your purchase. After 365 days, you will get 50% discounts for updating.

Money Back Guarantee
Full refund if you fail the corresponding exam in 60 days after purchasing. And Free get any another product.
Security & Privacy
We respect customer privacy. We use McAfee's security service to provide you with utmost security for your personal information & peace of mind.
